
Free guide to practical design of OT networks that do not stop production lines.


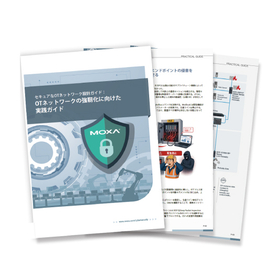
We will provide a document summarizing the key points for strengthening the OT network without stopping operations by reviewing the risks associated with connected devices, wireless connections, and remote access.
The OT network can pose risks from unexpected sources due to connections with IT environments and external services, wireless LANs, and the IPification of legacy devices. To ensure stable operation of equipment, it is important to have a network design that not only eliminates threats completely but also minimizes the impact in the event of a breach. The "Secure OT Network Design Guide" we are presenting addresses five risk scenarios anticipated in the operations of smart factories, explaining each risk and the countermeasures provided by Moxa. It allows for a concrete examination of easily overlooked issues such as boundary-less networks, unmanaged ports and devices, wireless networks, legacy equipment and vendor connections, and unnoticed configuration changes. Please utilize the tips provided for network segmentation, access control, protection of connection points, and review of monitoring and management in light of on-site operations. It also highlights risk factors that can be addressed without halting production lines. We encourage you to download the document as a first step in understanding the current state of your OT network and considering measures for its fortification.
basic information
**Secure OT Network Design Guide: A Practical Guide to Strengthening OT Networks** As connectivity in smart factories increases, unmanaged ports, unregistered devices, wireless LANs, remote maintenance connections, and unnoticed configuration changes can become unexpected entry points for intrusions. This document explains five risk scenarios that can occur in factory operations, detailing what might happen on-site and what countermeasures can be considered. You can specifically identify easily overlooked issues such as the expansion of impacts when network boundaries are unclear, device connections to unused ports, access to control networks via wireless, management of legacy devices and vendor connections, and oversight of configuration changes. In addition to examples of countermeasures for each scenario, it includes guidance on prioritizing boundary identification, separation using VLANs and ACLs, disabling unused ports, and points for access control and monitoring. This practical guide helps you understand risk factors that can be addressed without stopping production lines and encourages you to consider where to reassess your network. It is intended to assist in understanding the current state of OT networks and in exploring measures for strengthening them.
Price information
For consultations on OT security, product selection, implementation, and after-support, please contact IBS Japan!
Price range
Delivery Time
Model number/Brand name
Moxa OT Security Solutions
Applications/Examples of results
This is a document that we would like such customers to read: - Those who want to consider security measures for OT networks. - Those whose connections with IT, cloud, and external services are increasing. - Those who are concerned about managing unregistered devices and unused ports. - Those who want to review wireless LAN and remote connections from maintenance vendors. - Those who want to reduce risks while operating legacy equipment. - Those who want to know about measures that can be implemented without stopping the production line. - Those who want to strengthen OT security design as equipment manufacturers or system integrators. *Please see below for Moxa products that can be utilized for the OT security measures introduced in this document.
Line up(7)
| Model number | overview |
|---|---|
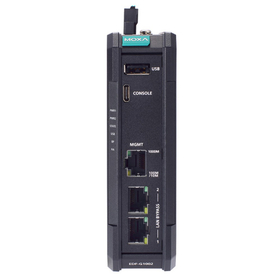
| EDF-G1002-BP Series | 2-port gigabit industrial LAN firewall, supports IPS/IDS and DPI for industrial protocols, equipped with Gen3 LAN bypass, minimizes impact on existing networks with BITW implementation. |
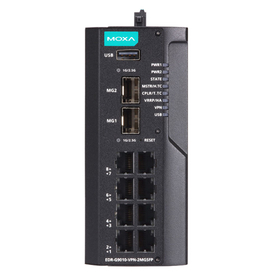
| EDR-G9010 Series | 8-port GbE copper + 2-port GbE SFP, integrated firewall/NAT/VPN/router/switch functions, supports IPS/IDS and DPI, certified with IEC 62443-4-2 Security Level 2. |
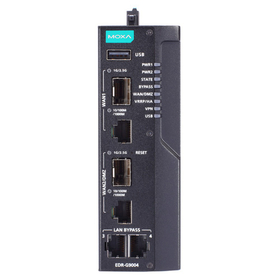
| EDR-G9004 Series | 2-port GbE copper + 2-port GbE copper/SFP combo, integrated firewall/NAT/VPN/router functions, equipped with Gen3 LAN bypass, supports IPS/IDS and DPI for industrial protocols. |
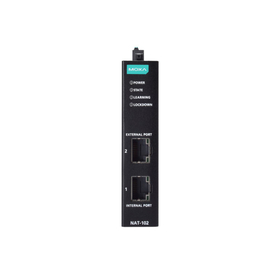
| NAT-102/108 Series | 2-port / 8-port industrial NAT device, supports 1-to-1 and N-to-1 NAT as well as port forwarding, learns the IP/MAC addresses of connected devices with an automatic learning lock function, compact design. |
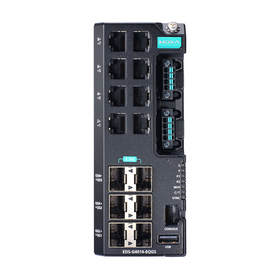
| EDS-4000/G4000 Series | Industrial managed switches with IEC 62443-4-2 certification, a portfolio of 68 models, supporting up to 90W of 802.3bt PoE and 2.5GbE, with wide temperature models available. |
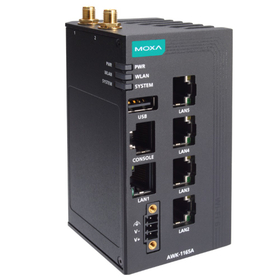
| AWK-1165A Series | 5-port gigabit Ethernet built-in industrial Wi-Fi 6 access point, dual-band support with up to 1,201 Mbps, WPA3 compatible, -T model operates at -40 to 75°C. |
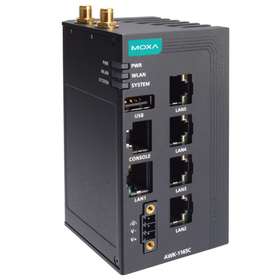
| AWK-1165C Series | 5-port Gigabit Ethernet built-in industrial Wi-Fi 6 client, dual-band support with up to 1,201 Mbps, client-based Turbo Roaming and WPA3 support, -T model operates at -40 to 75°C. |
catalog(1)
Download All Catalogs
Recommended products


Distributors

IBS Japan, with the motto "Supporting the IT transformation of industries that sustain our lives," is engaged in global business development in various industrial IT fields, focusing primarily on industrial networks. We carefully address the unique needs of each customer and provide comprehensive solutions that integrate the extensive knowledge and know-how we have cultivated in the industrial sector, thereby enhancing the efficiency and productivity of our customers' businesses. Together with our customers, we research high-level technologies and products recognized worldwide, and we propose solutions backed by solid technology and proven results every day.