
Reasons why SMS and app OTP cannot be prevented.


Real-time phishing attack countermeasures! Reasons why SMS and app OTPs cannot prevent them and case studies.
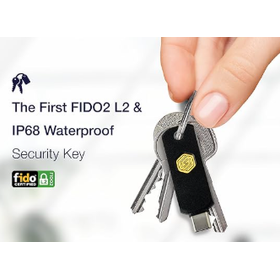
We would like to introduce a case study on the implementation of the Swissbit iShield Key 2 FIDO2. There was a challenge in that SMS authentication and TOTP (one-time codes) from authentication apps are vulnerable to real-time phishing attacks (AiTM: Adversary-in-the-Middle), where attackers can spoof legitimate login pages and relay the OTP entered by users in real-time. In this case study, by introducing this product, which can operate as an authenticator independent of the device, we achieved authentication that separates the dependencies. [Challenge] ■ SMS authentication and TOTP (one-time codes) are vulnerable to real-time phishing attacks (AiTM: Adversary-in-the-Middle). *For more details, please download the PDF or feel free to contact us.
basic information
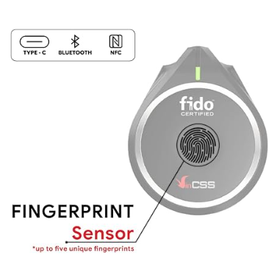
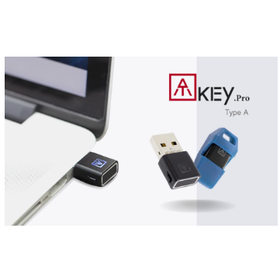
【Product Specifications】 ■Supported Standards: FIDO2 / CTAP2.1 / WebAuthn, FIDO U2F ■Connection: USB Type-A / USB Type-C (select at purchase), NFC compatible *For more details, please download the PDF or feel free to contact us.
Price range
Delivery Time
Applications/Examples of results
For more details, please download the PDF or feel free to contact us.
catalog(1)
Download All Catalogs
Recommended products


Distributors

What security is suitable for remote work? How should we respond to Salesforce's multi-factor authentication (MFA)? What is single sign-on (SSO)? You can find security solutions that are appropriate for each company.