
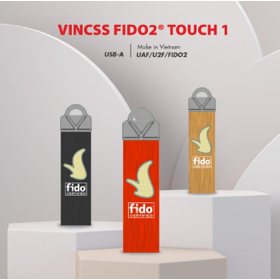
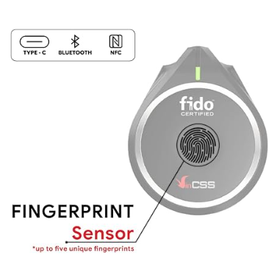
Authentication methods that meet/do not meet the requirements for mandatory phishing-resistant MFA.


Responding to Salesforce's mandatory MFA for phishing resistance!
Since February 2022, Salesforce has made multi-factor authentication (MFA) mandatory for all users in its terms of service. In addition, a two-step enhancement was implemented in 2026. MFA that is resistant to phishing is required for system administrators and "privileged users" with strong permissions. MFA in a format recognized by Salesforce is also mandatory for other internal users. Both requirements have been applied to the release groups in Japan and South Korea as of September 1, 2026. The first step is to identify your company's privileged users. Privileged users will be required to use MFA that is resistant to phishing (either a security key, built-in authenticator, synchronized passkey, or certificate-based authentication). *For more detailed information, please refer to the related links. For further details, you can download the PDF or feel free to contact us.*
basic information
*You can view the detailed content of the article through the related link. For more information, please download the PDF or feel free to contact us.*
Price range
Delivery Time
Applications/Examples of results
*You can view the detailed content of the article through the related link. For more information, please download the PDF or feel free to contact us.*
catalog(1)
Download All Catalogs
Recommended products


Distributors

What security is suitable for remote work? How should we respond to Salesforce's multi-factor authentication (MFA)? What is single sign-on (SSO)? You can find security solutions that are appropriate for each company.